
Description
The Senders tab controls which senders in your organization a policy set applies to. You can apply the policy set to everyone, or scope it to specific senders, groups, or an advanced query based on user attributes.
How to access it
To access the Senders tab:
- From the Tamper Detection page, select Manage on the relevant policy set.
Select the Senders tab.
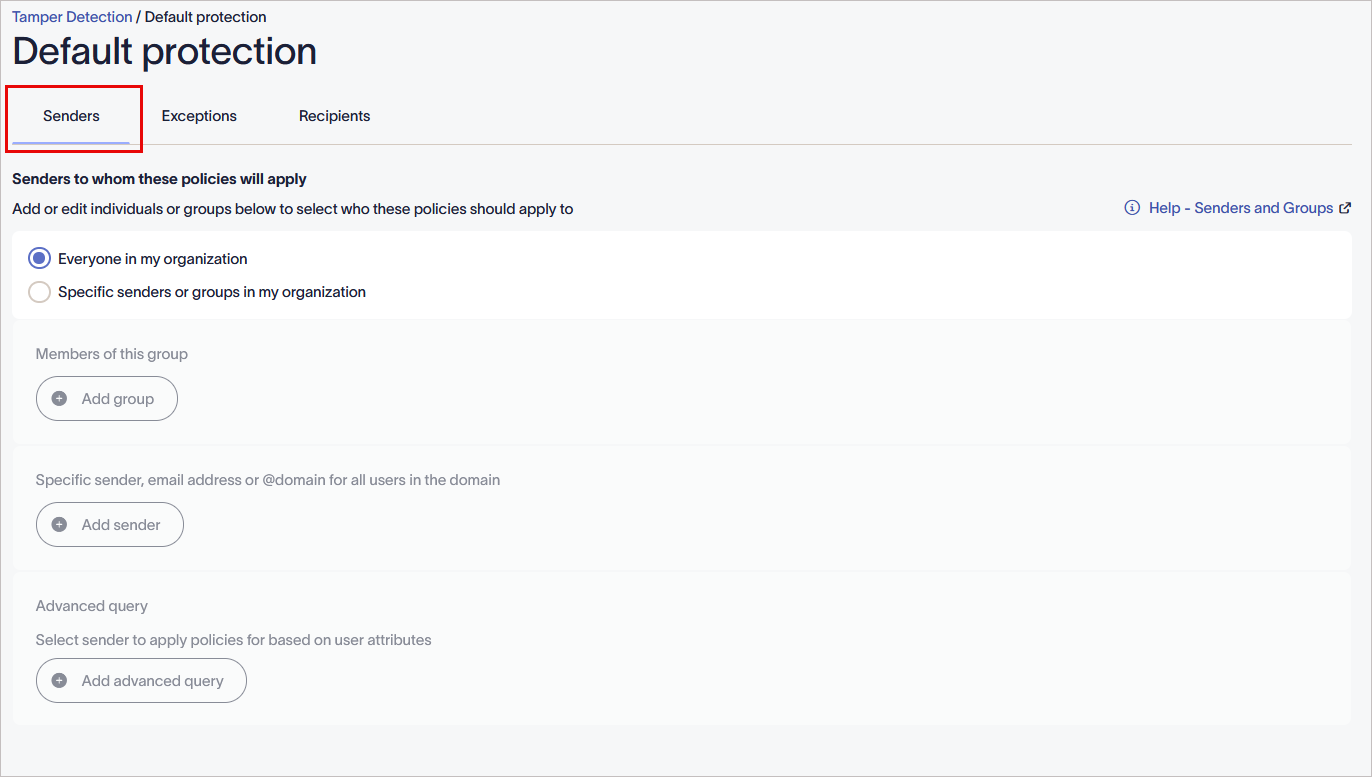
Select the Senders tab.
Defining which sender this policy applies to
Use the configuration options in the Senders tab to include senders or groups in a policy set.
Select an option below to view the related instructions:
To apply the same policy to all users within your organization:
- Select the Everyone in my organization radio button.
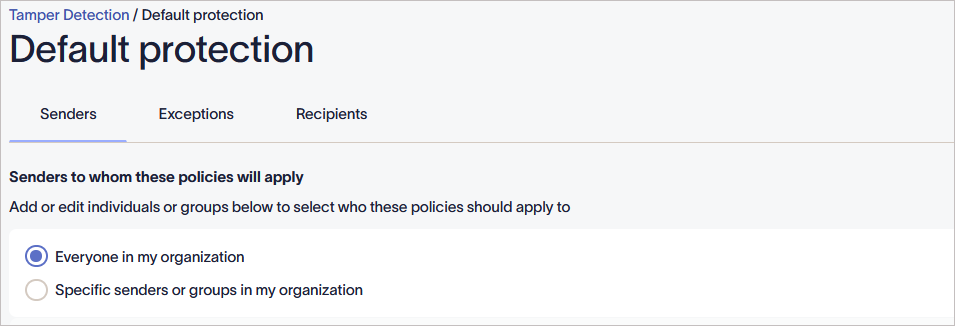
When the Everyone in my organization option is selected, no other sender rules apply.
When this option is selected, the other Sender options are disabled.
- Select the Specific senders or groups in my organization radio button.
This option applies the policy set to members of a group you've configured in your Microsoft or Google Directory. For information on creating groups, see How to create a mail-enabled security group.
To add a group:
- Select Add group.
-
Under Members of this group, enter the group name. The predictive text field displays names as you type.
NOTE: Only the contact details of mail-enabled security groups and distribution groups synced with Exclaimer are available to select. - To add another group, select Add group. To delete a group, select the bin icon
 .
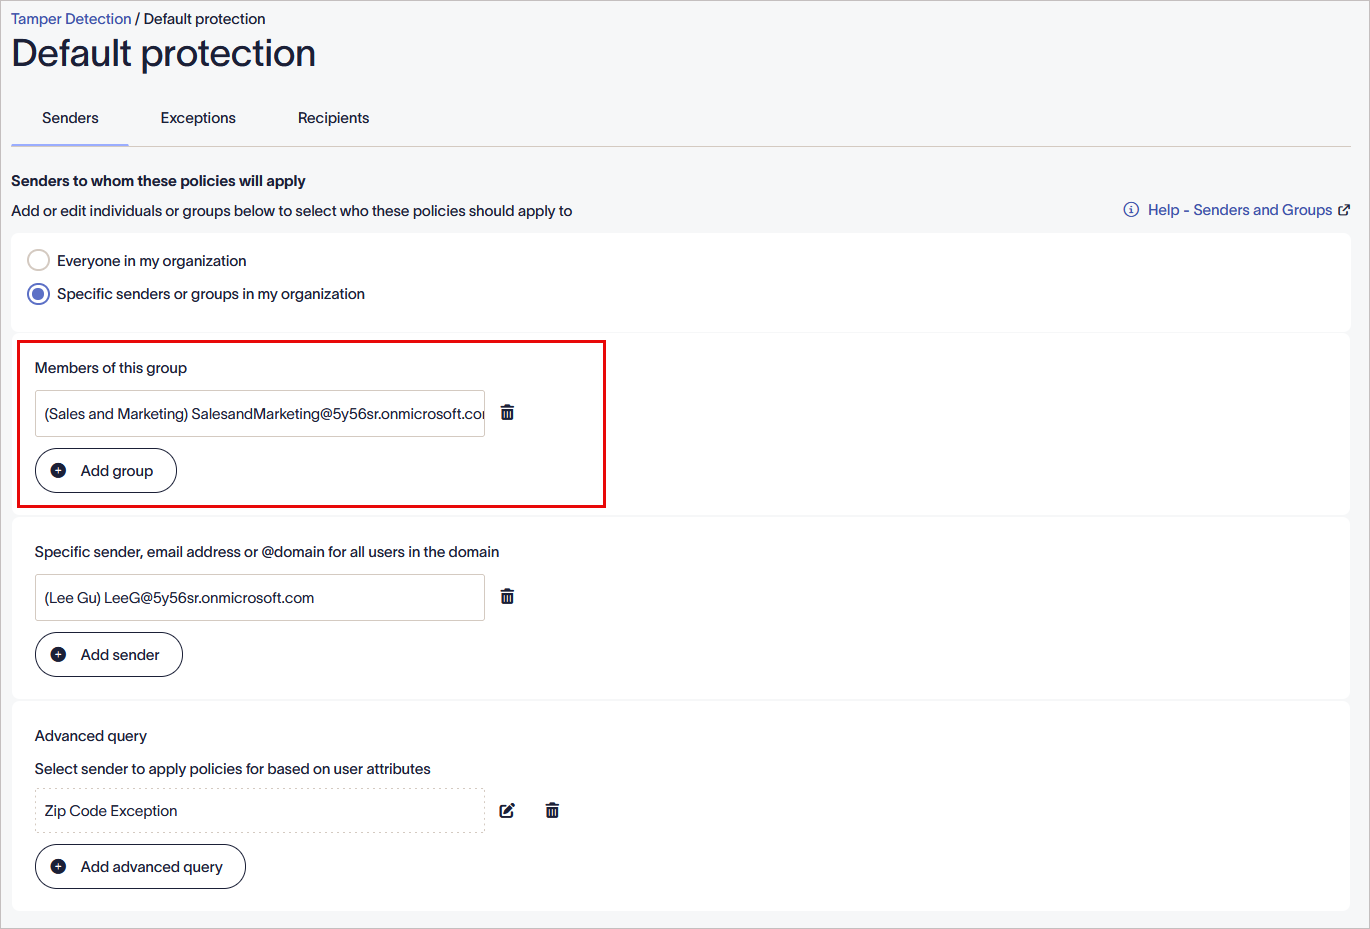
Members of this group.
- In the unsaved changes banner, select Save to apply your rules, or select Cancel to revert all changes.
This option applies the policy set to manually selected users or domains. Using an @domain applies the policy set to all users with that domain in their email address.
To add a specific sender, email address or @ domain:
- Select Add sender.
-
Enter the specific sender name, email address or domain. The predictive text field displays names as you type.
Tip! You can also use a wildcard (*) when entering an email address or domain name. A wildcard represents any available characters attached to the complete text. Exclaimer allows for any number of characters to be substituted for a wildcard.
Some examples using a wildcard are:
*@greenorg.net - this would include any email addresses that are followed by '@greenorg.net'.
@exclaimer.* - this would include any domains attached to Exclaimer email addresses.
@*.de - this would include any domains that are followed by .de. - To add another sender, select Add sender. To delete a sender, select the bin icon .
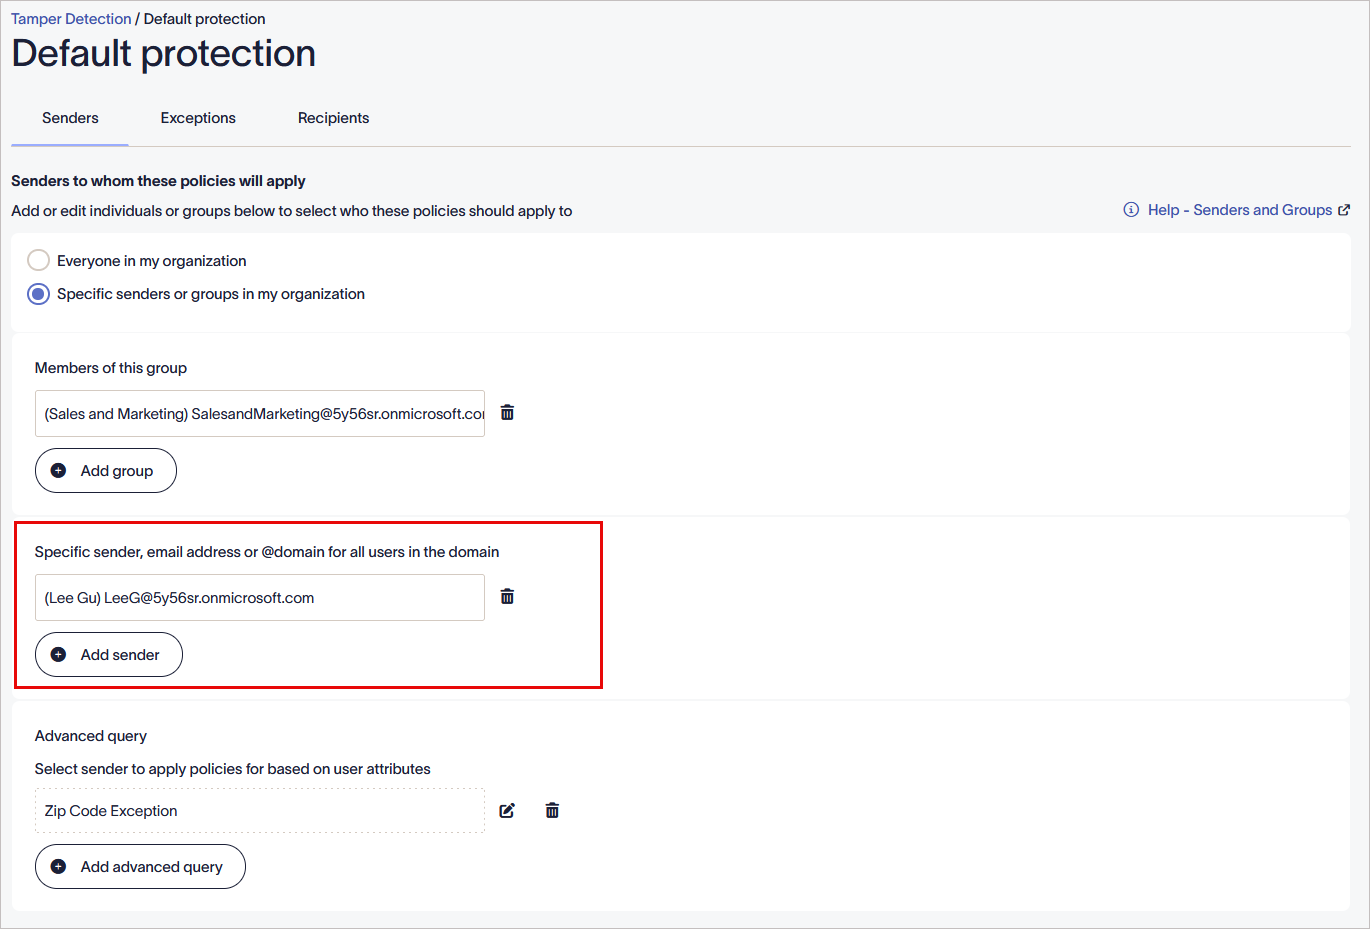
Specific sender, email address or @domain for all users in the domain.
- In the unsaved changes banner, select Save to apply your rules, or select Cancel to revert all changes.
This option applies the policy to senders based on user attributes that are assigned to your users in the Microsoft or Google directory.
To add senders with specific attributes:
- Select Add advanced query.
The Advanced query window is displayed.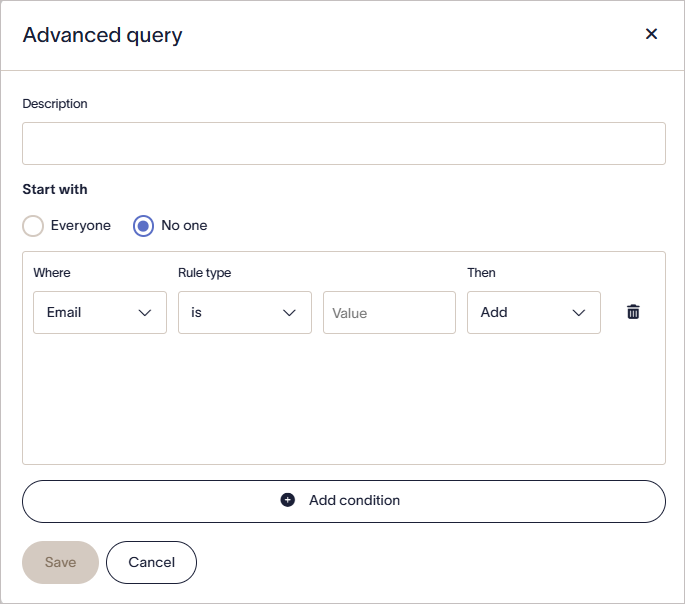
The Advanced query window.
- In Description, enter the text to name your query. This description appears in your Senders tab to identify the Advanced Queries you have set.
- Under Start with, select either:
No one to start the query with no users and add matched users.
or
Everyone to start the query with all users and remove matched users.
- From the Where drop-down, select a user attribute field to check the data for.
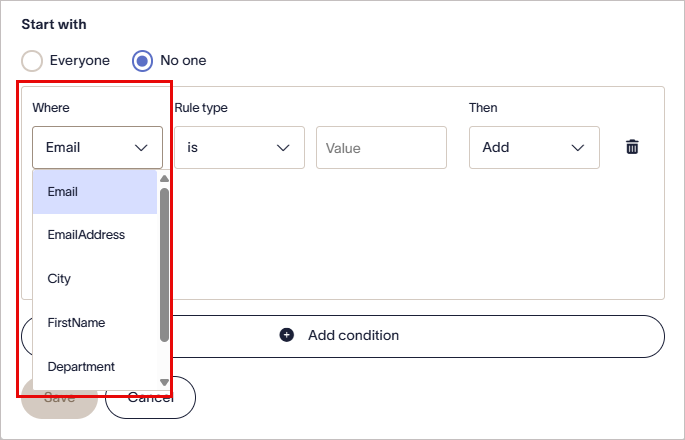
From the Where drop-down, select a user attribute field to check the data for.
- From the Rules type drop-down, select one of the following options to set how your attribute data is checked:
is - the attribute data must completely match the following text.
contains - the attribute data must have the following text somewhere within it.
starts with - the attribute data must begin with the following text.
ends with - the attribute data must end with the following text.
is not - the attribute data must not be the same as the following text.
does not contain - the attribute data must not have the following text anywhere within it.
does not start with - the attribute data must not begin with the following text.
does not end with - the attribute data must not end with the following text.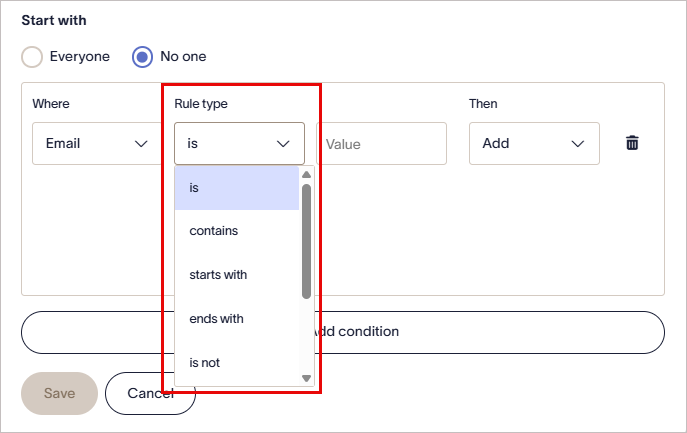
From the Rules type drop-down, select an option.
-
In the blank text box, enter the comparison text. This field is not case-sensitive.
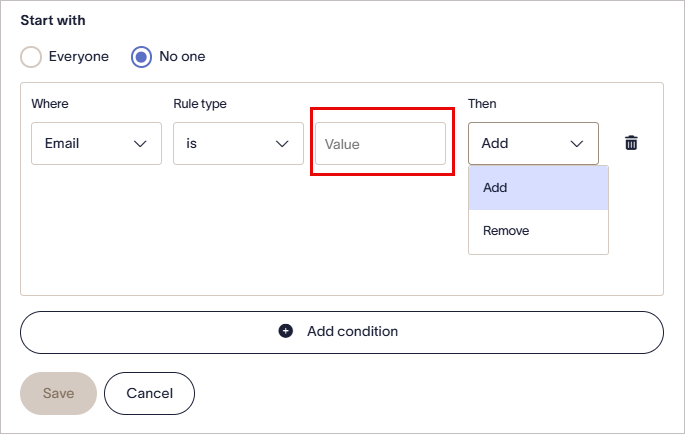
Enter a comparison value.
NOTE: Your query uses the options and text to search for users that match the criteria and either set or eliminate them as senders.
Some examples of queries are:
Start with: No one, Then: Add > User Where: JobTitle > includes > Sales will add only users with the term Sales anywhere in their job title as senders.
Start with: Everyone, Then: Remove > User Where: EmailAddress > ends with > example.com will add everyone as a sender except for any users whose email address ends with example.com. - From the Then drop-down, select either Add or Remove to include or exclude the matching users.
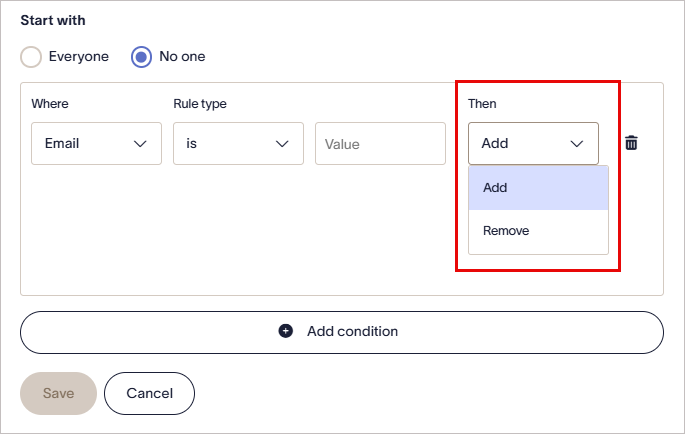
From the Then drop-down, select either Add or Remove to include or exclude the matching users.
-
Select Add Condition to add further rows (maximum ten).
NOTE: Conditions are processed in order, and conflicting conditions are resolved by priority — higher rows take precedence. -
Select Save to save the query and return to the Senders tab. Your query is displayed with its description.
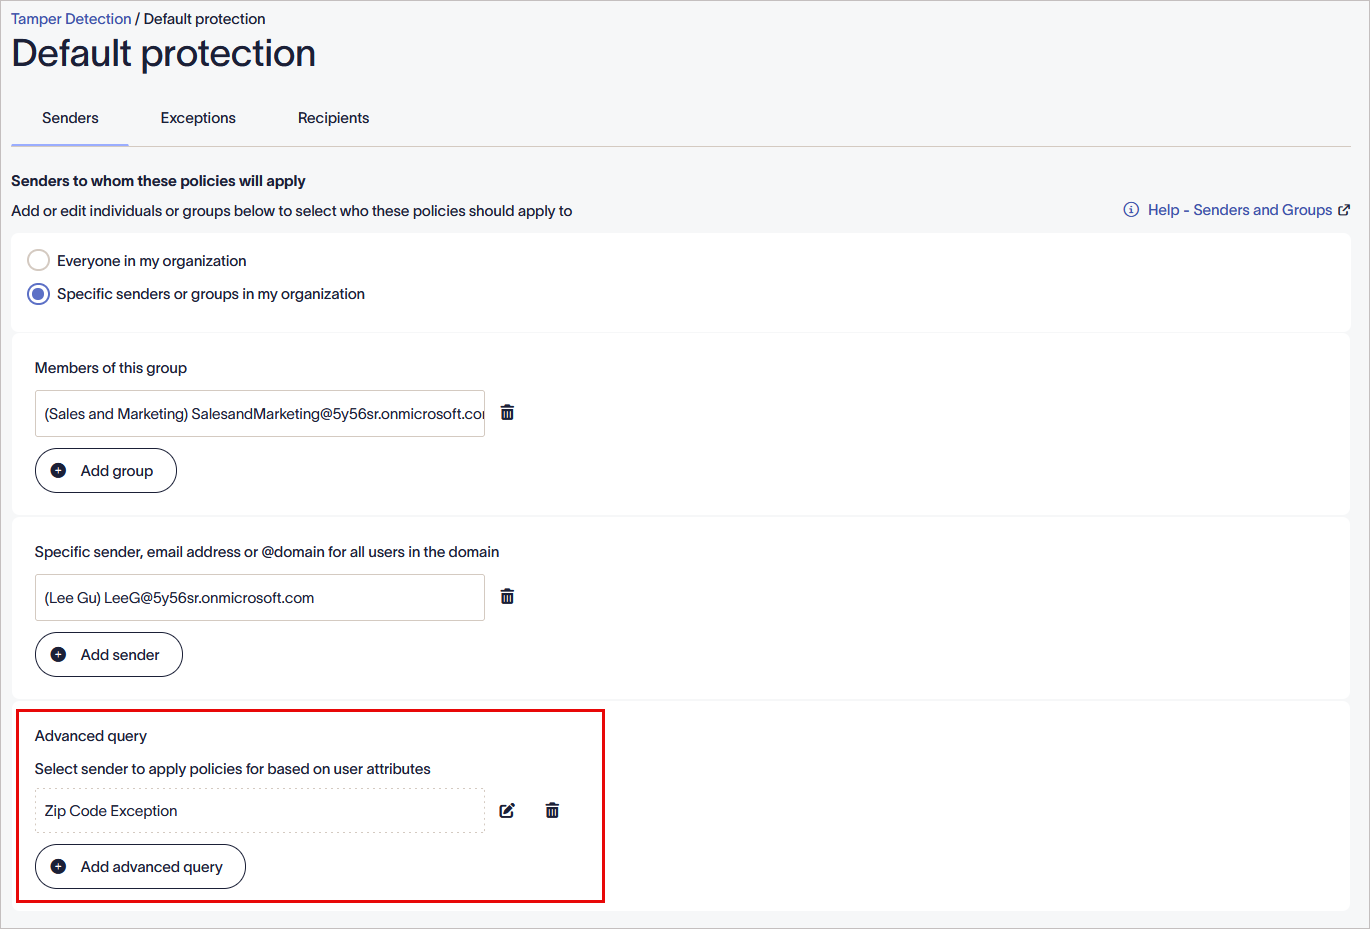
Query description in the Senders tab. - Select the pencil icon
 to edit the advanced query. Select the bin icon to delete the advanced query.
- In the unsaved changes banner, select Save to apply your rules, or select Cancel to revert all changes.